Quality & security testing for ASP.NET Core

ASP.NET Core Code & Website Security Audit Platform.

Scan ASP.NET Core and C# projects or live websites for security vulnerabilities, code quality issues, exposed secrets, and configuration risks. Get AI-assisted recommendations, compliance mapping, and professional PDF audit reports with version tracking and live scan progress.
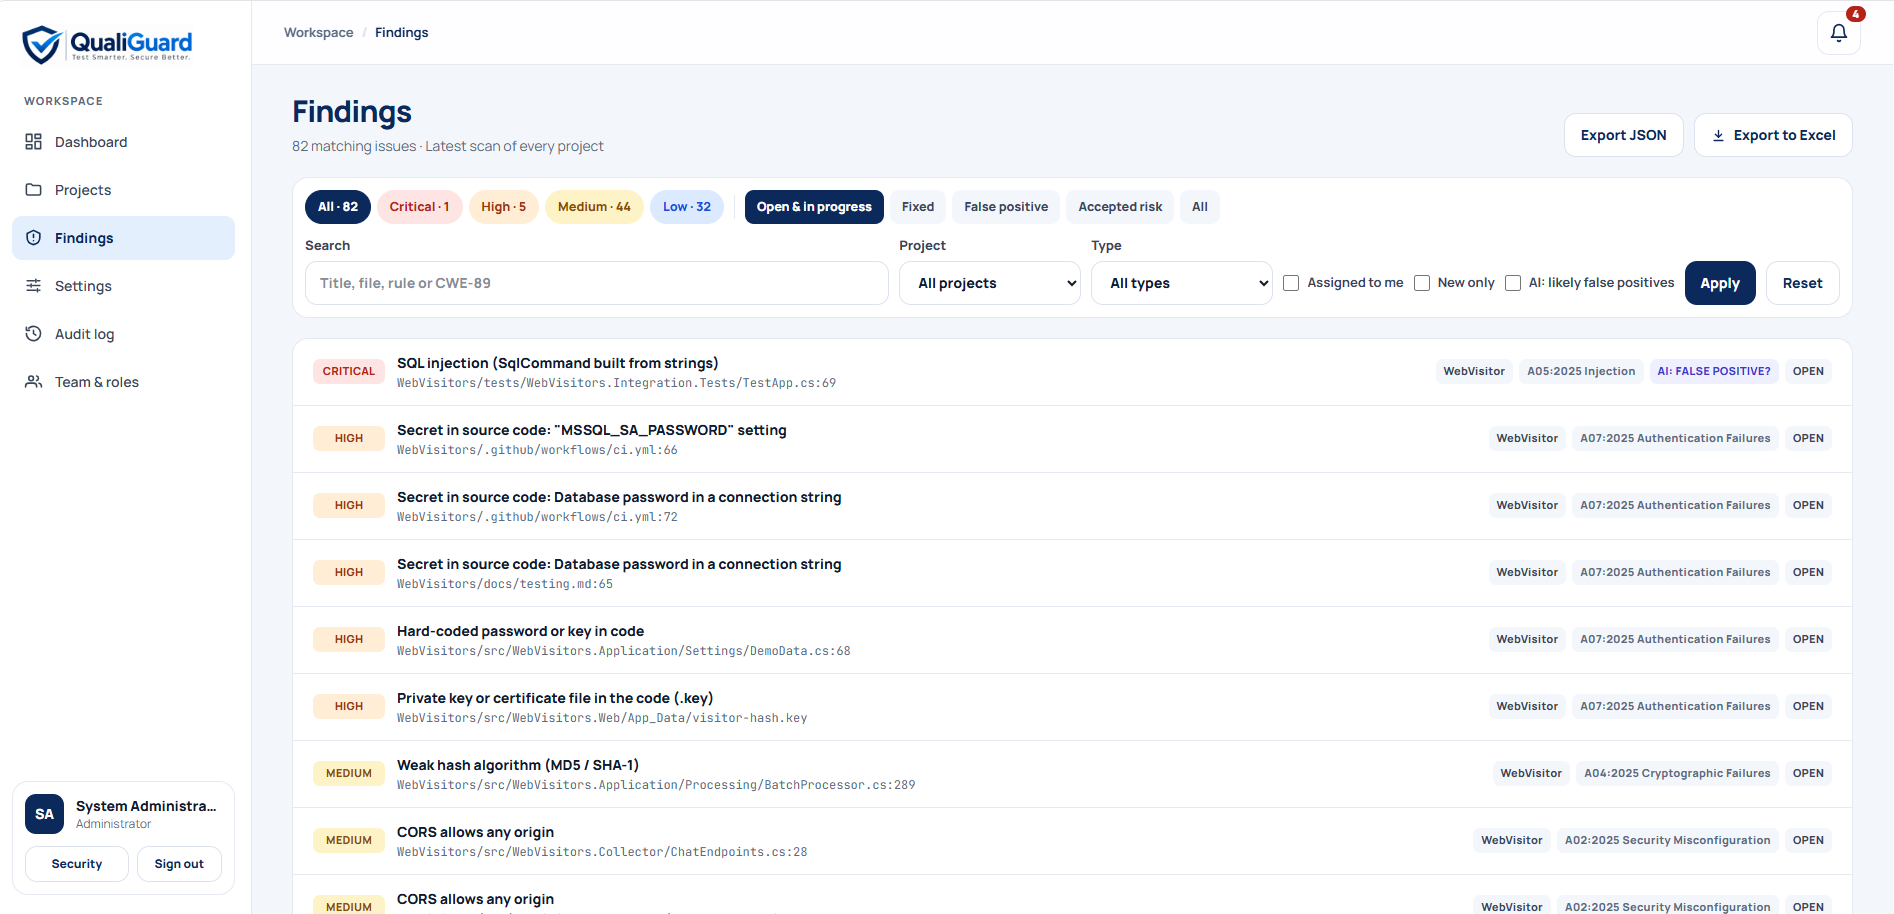
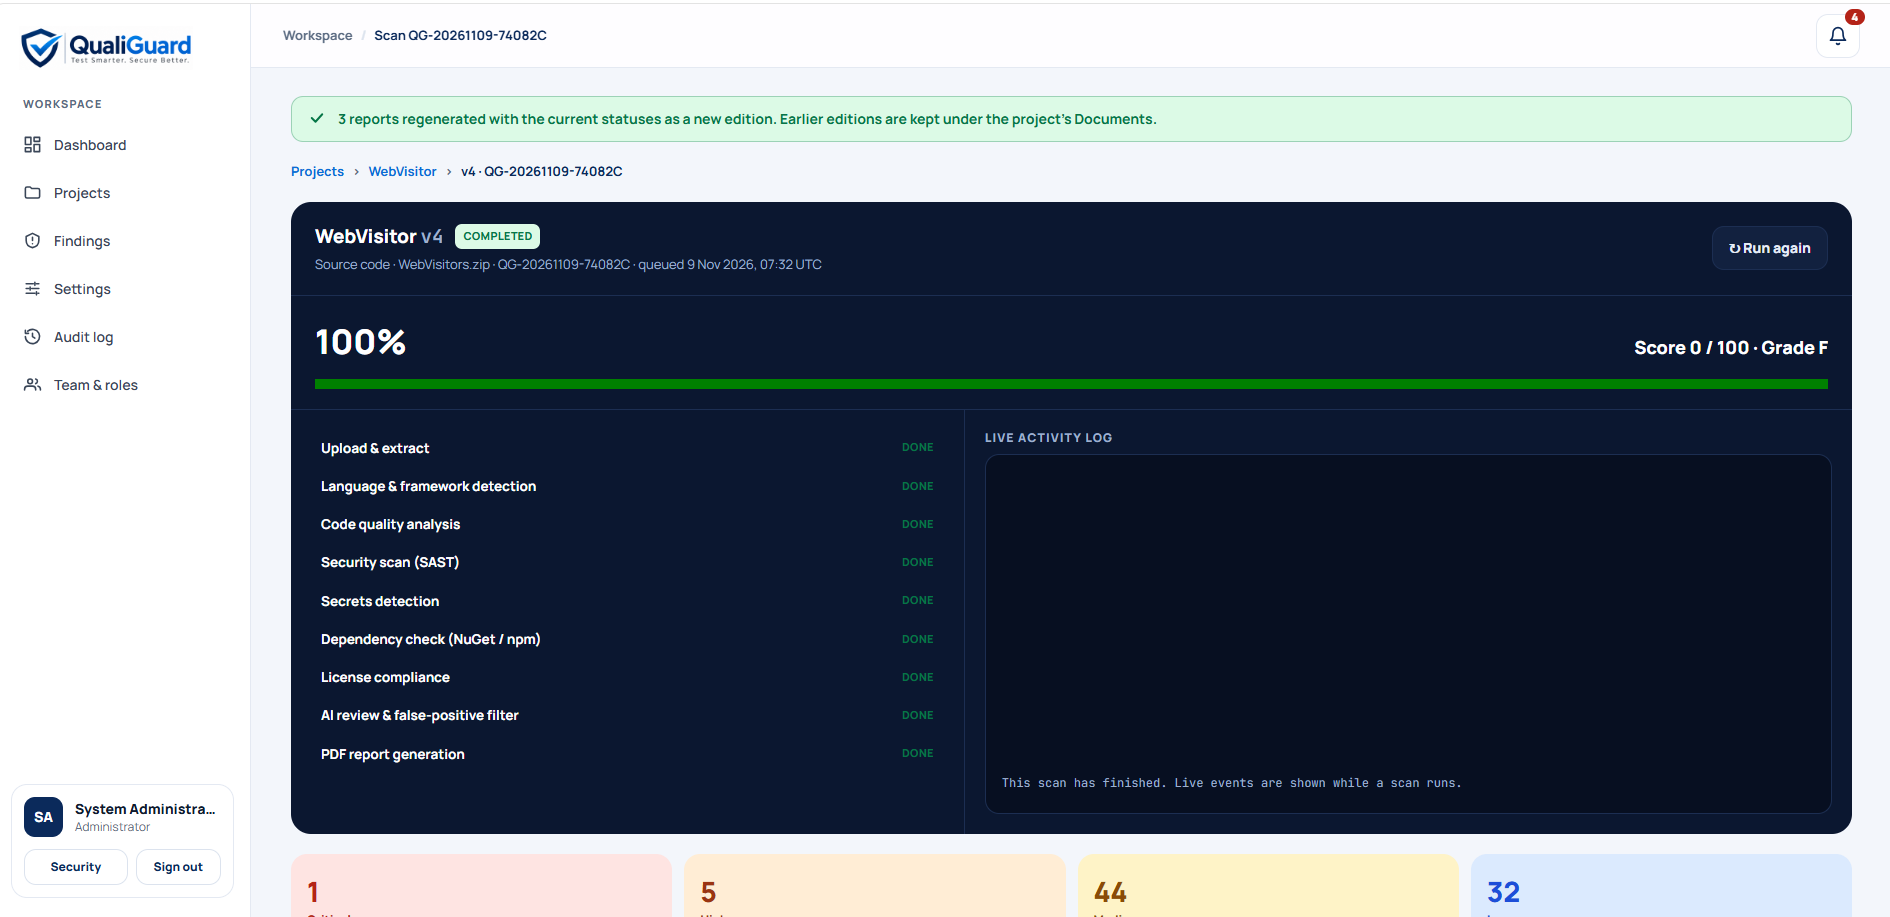
QualiGuard live scan view
LIVE ACTIVITY{{ run.pct }}
› {{ l.msg }}
{{ cmpGrade }}
QUALITY SCORE
Graded A–F
{{ s.v }}
{{ s.l }}
~{{ statRules }}
Built-in Roslyn rules
C# · Razor · JS · config
0–{{ statScore }}
Score with grades A–F
{{ g.l }}
{{ gaugeGrade }}
{{ statFw }}
Compliance frameworks
mapped on every finding
{{ f.l }}
{{ statPdf }}
PDF reports per scan
{{ pdfLabel }}
Features

Code, website and AI review in one run.

Lite mode works without Docker. Turn on Docker mode for Semgrep, Gitleaks, Lizard, jscpd and active OWASP ZAP tests.

{{ fCur.n }} / 06
67 public Visit Find(string id) {
68 var sql = "SELECT * FROM Visits WHERE Id=" + id;
69 using var cmd = new SqlCommand(sql, conn);
70 return Map(cmd.ExecuteReader());
71 }
CRITICALCWE-89A05:2025 Injection
{{ s.t }}
{{ s.f }}
HIGH
{{ d.label }}{{ d.status }}
Advisories via OSV.dev
https://webvisitor.exampleverified
{{ c.mark }}{{ c.label }}
AI fixWeak hash algorithm (MD5 / SHA-1)
- using var h = MD5.Create();
+ using var h = SHA256.Create();
MD5 is broken for integrity checks. SHA-256 keeps the same API shape.
{{ v.l }}

{{ fCur.title }}

{{ fCur.body }}

How it works

Watch every step of the scan as it happens.

{{ s.title }}
WebVisitor v4{{ run.label }}
{{ run.pct }}
{{ p.label }} {{ p.status }}
Live activity log
{{ l.t }}{{ l.msg }}
›
{{ s.v }}
{{ s.l }}
Screens

Inside the workspace

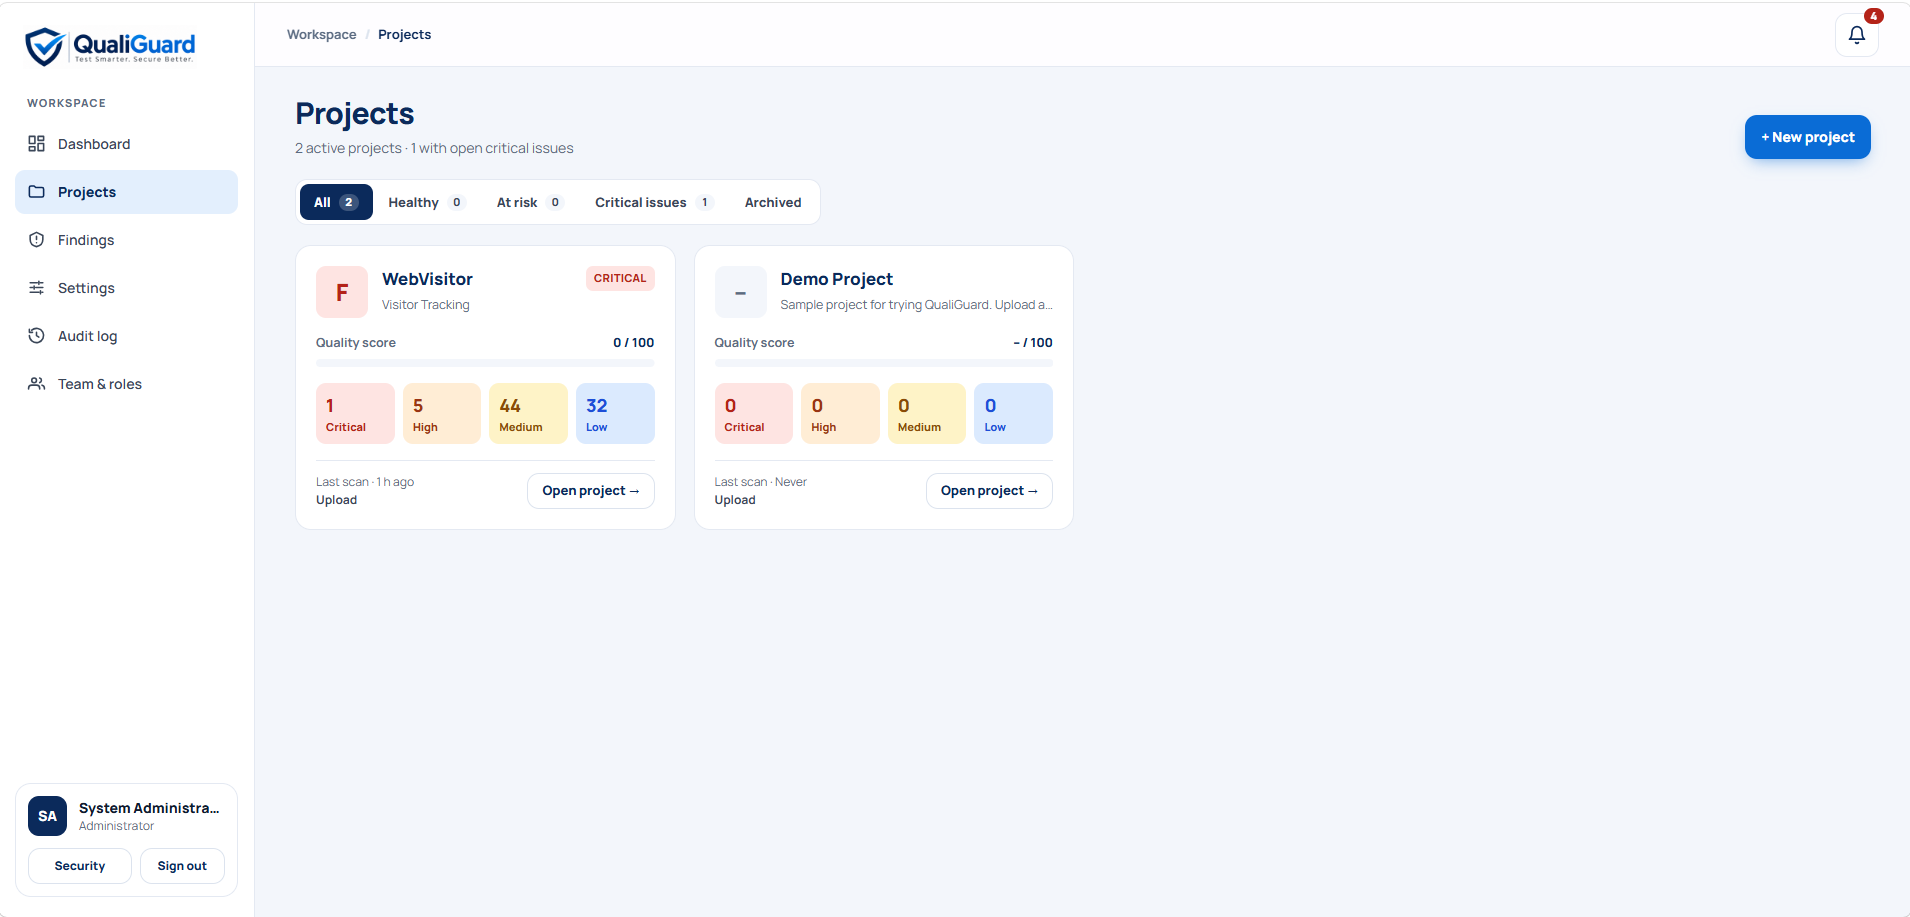
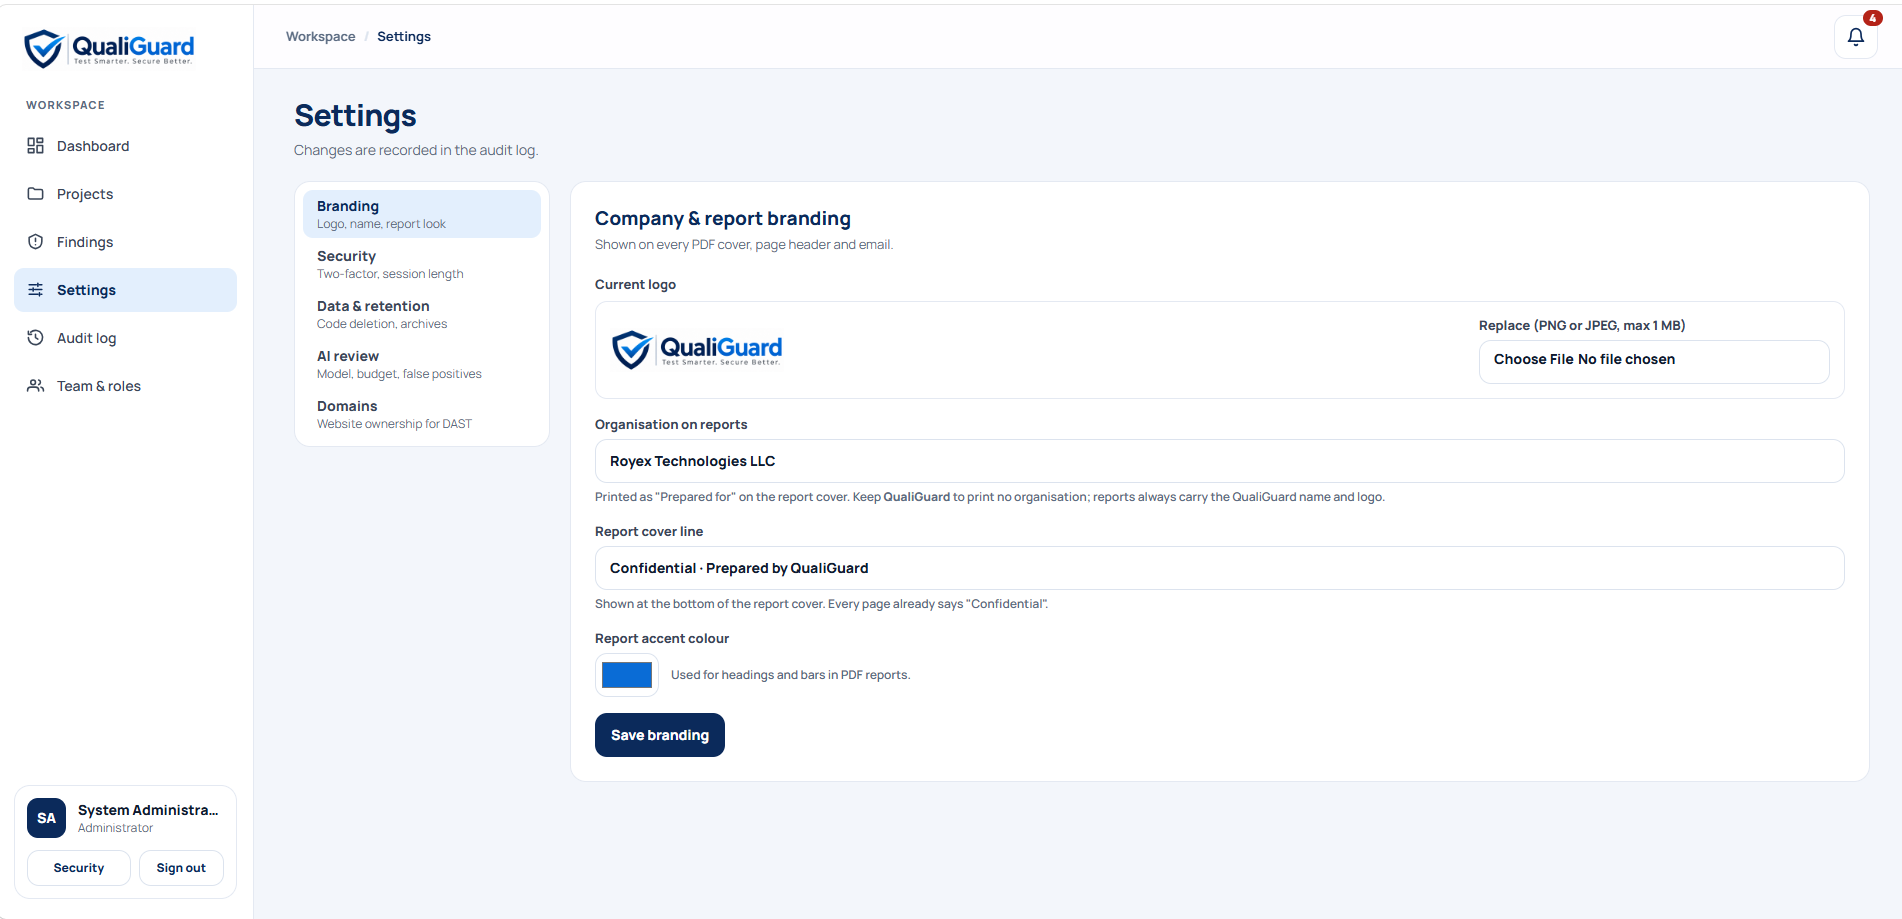
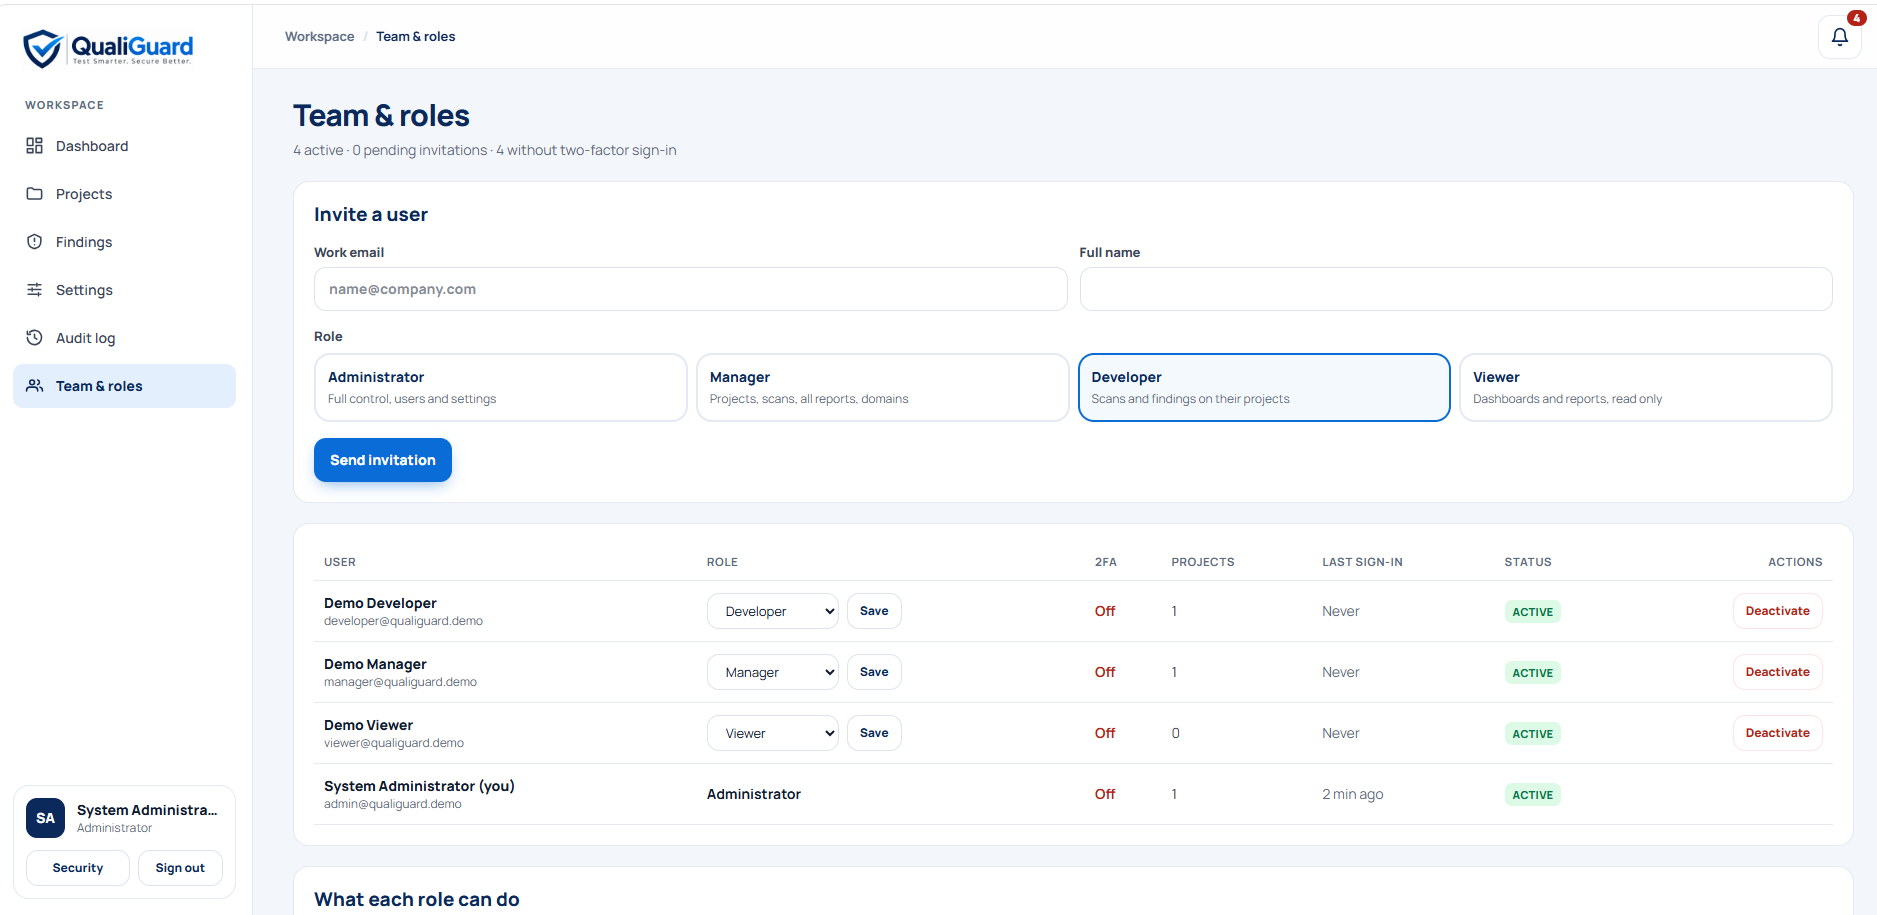
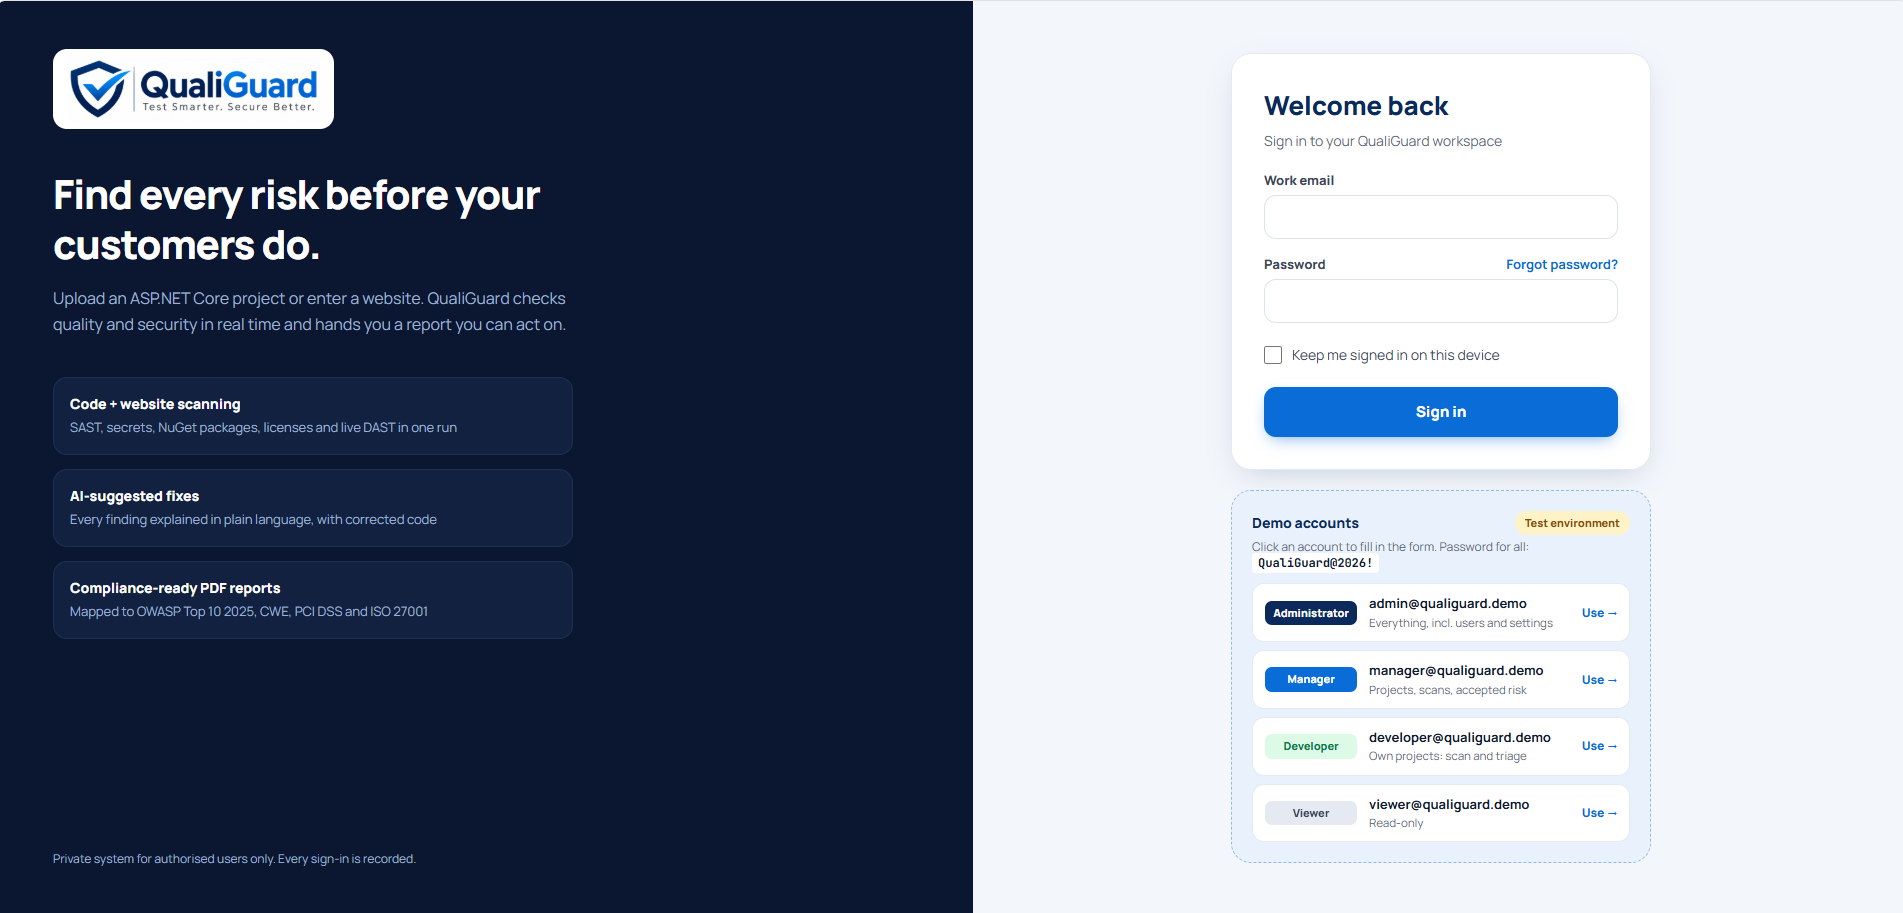
QualiGuard scan screenQualiGuard projects screenQualiGuard findings screenQualiGuard settings screenQualiGuard team screenQualiGuard login screen
{{ active.big }}

{{ active.title }}

{{ active.body }}

{{ active.num }}
Your code, your AI agent Full source

Extend QualiGuard with Claude, Codex or Antigravity.

QualiGuard follows a Clean Architecture layout, so an AI coding agent can find its way around quickly. Open the solution and ask for new scan rules, different report layouts or extra workspace screens.
QualiGuard
{{ a.maker }}

{{ a.name }}

{{ a.body }}

› {{ a.typed }}
Scoring & compliance

A score your auditors understand.

Every finding gets a severity and maps to the standards you report against. Each scan is a version, so you can follow the score trend and see new and fixed issues between runs.

{{ r.s }} {{ r.t }} {{ r.c }}
{{ cmpGrade }} GRADE · 0–100
{{ n.name }}
{{ n.map }}
Reports

Three PDFs, ready when the scan ends.

Executive, Technical and Comparison PDFs in the QualiGuard design, created automatically after every scan, in your own branding. Every edition is kept.

{{ c.kind }} report
WebVisitor v4
Confidential · Prepared by QualiGuard
Team & security

Four roles, one audit trail.

{{ roleCur.name }}
{{ roleCur.desc }}
{{ roleCur.count }} / 6 permissions
{{ p.label }} {{ p.mark }}
Security controls{{ secOn }} / 5 on
{{ c.label }}
AI review
Plain-language findings with corrected code.
Anthropic Claude API (Sonnet / Haiku). The API key is managed in Settings and stored encrypted.
{{ a.label }}
Tech stack

Built on ASP.NET Core 10.

Clean Architecture solution, ready for Azure.

QUALIGUARD.SLN · CLEAN ARCHITECTUREDependencies point inward →●
{{ r.name }}
{{ ringCur.name }}
{{ ringCur.desc }}
{{ t.k }} {{ t.v }}
Live demo

Sign in and run a scan yourself.

Each demo account shows a different role. Password for all accounts: QualiGuard@2026!

qualiguard.demo{{ demo.path }}
Demo accounts
QualiGuard
Welcome back
Sign in to your QualiGuard workspace
Work email
{{ login.email }}
Password
{{ login.pass }}
{{ demo.btnLabel }}
QualiGuard projects workspace
✓Signed in as {{ demo.role }}